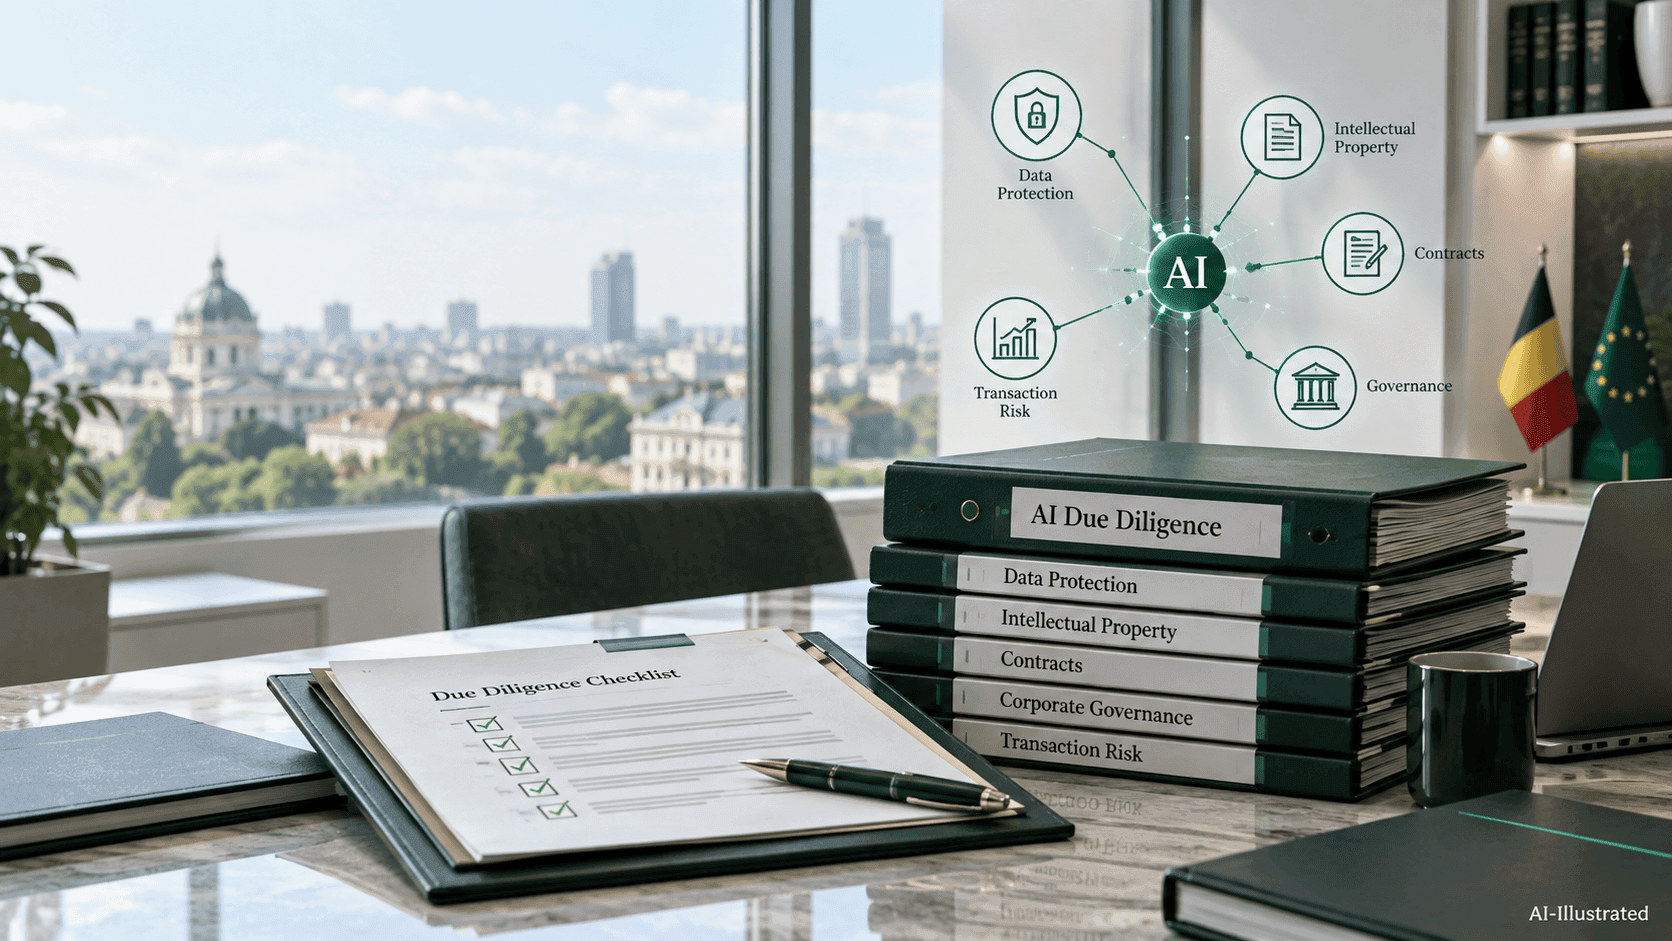
AI due diligence checklist for foreign investors assessing a Romanian company

AI Due Diligence in Romania: What Foreign Investors Should Check

Foreign investment • AI governance • Romania

AI due diligence in Romania asks whether a target company’s AI use, data, contracts and public claims support the investment case. It is not a technical demonstration of a model and it is not a generic AI policy review. For a buyer, investor or lender, the question is whether the target has identified the systems it uses, can lawfully operate them, owns or can use the assets it relies on, and has a credible plan for the risks that will remain after closing.

What is AI due diligence in a Romanian transaction?

AI due diligence is a transaction-focused legal and commercial review. It identifies whether the target’s use of AI creates liabilities, restrictions, missing rights or implementation costs that could affect price, risk allocation or post-closing operations.

For a Romanian target, the review should cover the target’s Romanian operations and any AI outputs used in the European Union. The EU AI Act is directly applicable across the EU and operates alongside the GDPR where personal data is processed. A seller’s statement that it uses only a third-party AI tool does not end the inquiry: the target may still be a deployer, customer, controller, employer or regulated business with its own duties.

This guide has a different purpose from our analysis of AI vendor contracts in Romania, which focuses on the agreement with a supplier, and from DPIA vs FRIA in Romania, which focuses on assessment triggers for a deployment. Here, the investor is deciding what must be verified before, at and after a deal.

Start with the target’s actual AI footprint

Do not begin with a broad question such as “Does the company use AI?” Ask what system or model is used, for which decision, with which data, by whom, and whether the target sells, deploys, develops, fine-tunes or merely accesses the tool.

A useful data-room request separates customer-facing products from internal tools. It should identify models, APIs, software providers, hosting and cloud dependencies, integrations, datasets, prompts or knowledge bases, material outputs, users and the decisions influenced by each use case. The inventory should also record planned products or features that have not yet launched but are material to the investment thesis.

Deal-side navigator

Select a deal question to see the first evidence to request

Click or tap a card. Keyboard users can Tab to a card and press Enter or Space. Each selection stays visible until you choose another one.

Business model and footprint

Request a system inventory, product descriptions, roadmaps, supplier contracts, architecture summary and evidence of the target’s material AI claims. Compare marketing language with the technology and operating model actually in use.

Which legal and commercial issues should an investor test?

Click or tap a row to highlight the diligence takeaway. On a small screen, swipe the table sideways.

AI due diligence matrix for a Romanian target
Review areaWhat to testPossible deal response
Whether the target’s product, sales material and internal inventory describe the same systems, functions, limits and dependencies.Correct the diligence scope, ask for technical confirmation and qualify representations that are broader than the evidence.
Whether a use case may be prohibited, high-risk, subject to transparency rules or linked to a general-purpose AI model supply chain.Obtain a classification record, identify compliance timing and budget for any remediation or implementation work.
Data flows, controller/processor roles, legal bases, Article 22 issues, DPIA screening, security measures and cross-border transfers.Require a privacy remediation plan, review the DPA and test whether the target can continue the relevant processing after closing.
Whether datasets, prompts, files or customer information may lawfully be used for development, fine-tuning, testing or supplier improvement.Limit or stop impermissible use, obtain consents or contractual permissions where appropriate, and reserve a specific risk allocation.
Ownership and licences for software, open-source components, models, training materials, brand assets, output and third-party claims.Confirm chain of title, address licence conflicts and tailor warranties or indemnities to the assets that support the valuation.
Model, cloud and subprocessor dependencies, location, termination, audit evidence, model changes and service continuity.Seek consent, amendment, transition assistance or a post-closing migration plan if a dependency cannot support the buyer’s intended use.
Policies, ownership, AI literacy, logs, testing, monitoring, incident response, complaint handling and escalation records.Set a post-closing governance plan with owners, deadlines and evidence requirements rather than relying on a generic policy.

The European Commission describes the AI Act as a risk-based framework for developers and deployers. It identifies employment, credit scoring and access to essential services among the examples that may be high-risk. See the Commission’s AI Act overview and application timetable.

AI Act review: classify before you value the risk

Do not treat “AI Act compliant” as a sufficient diligence answer. Contractual, sector-specific, data-protection and AI Act obligations must be assessed separately. The investor should identify the system, its intended purpose, the target’s role and the rules that apply now or later. The relevant date can affect both risk allocation and integration planning.

The AI Act’s prohibitions, AI literacy obligations, governance rules, GPAI-model obligations and transparency rules have different application dates from the rules for high-risk systems. The Commission states that Annex III high-risk use cases, including employment and credit-scoring examples, are scheduled to apply from 2 December 2027, while high-risk systems embedded in regulated products have a later date of 2 August 2028. A diligence report should distinguish obligations already applicable from future obligations that could require a funded implementation plan. At the time of publication, the applicable AI Act timetable should be verified against the latest EU legislation and implementation guidance, including the official AI Act Service Desk timeline.

The analysis should also ask whether the target is developing an AI system, placing it on the market, deploying it in its own business, importing it, distributing it or using a third-party service. These labels are not interchangeable with GDPR controller and processor roles. For the contract-facing part of that review, see AI Vendor Contracts in Romania.

GDPR and data review: look beyond the privacy policy

The decisive question is what happens to personal data at each stage of the AI lifecycle. A target may process personal data in training, testing, deployment, monitoring, logs, prompts, support and human review, even where the product is marketed as automated or anonymised.

The review should map the data categories, purposes, retention, recipients, access, transfer mechanisms and contractual roles. Where the use involves profiling, recruitment, credit, insurance, pricing or decisions that may significantly affect individuals, check the actual decision flow and safeguards rather than relying on a generic human-review statement. Article 35 GDPR requires a DPIA where processing is likely to result in a high risk to the rights and freedoms of natural persons; Article 22 has separate rules for certain solely automated decisions.

The European Data Protection Board has also confirmed that the anonymity of an AI model trained with personal data must be assessed case by case. That matters for a target relying on a statement that a model, dataset or output is anonymous. Read EDPB Opinion 28/2024. For the broader framework, see our guide to GDPR compliance when using AI in Romania.

Data, intellectual property and contract rights

AI value is often dependent on rights that sit outside the target’s own code. The investor should trace the legal basis for using data, third-party models, cloud infrastructure, open-source components, output and confidential information.

Review the complete contract suite, not only the signed master agreement. Order forms, online terms, acceptable-use policies, data-processing agreements, security schedules, open-source notices and API terms can all affect the target’s rights. In particular, check whether a provider can use customer or target data for model training, whether the provider can change the model or service unilaterally, and whether the target can export its data and configurations on exit.

Ownership language for AI-generated output should be read carefully. A contractual promise may create a licence or allocation between the parties, but it does not necessarily guarantee exclusivity or copyright protection in every output. The copyright status of AI-generated content may vary depending on the level of human creative input and the applicable jurisdiction. The review should identify the use the target needs to make of the output and whether third-party rights, human authorship requirements, confidentiality or contractual restrictions could limit that use.

What should the investor request in the data room?

  1. Request a current AI inventory. Include internal tools, customer-facing products, models, APIs, plugins, fine-tuning, integrations and material planned features.
  2. Obtain a use-case map. Record intended purpose, users, affected people, decisions, data inputs, outputs, human review and country of deployment.
  3. Collect AI governance records. Ask for role assessments, policies, training records, system documentation, risk logs, testing, monitoring and incident procedures.
  4. Review AI Act screening. Identify prohibited practices, potential high-risk systems, transparency obligations, GPAI dependencies and the applicable timetable.
  5. Map personal-data processing. Review privacy notices, legal bases, Article 22 analysis, DPIAs, processor arrangements, security controls and transfers.
  6. Trace data rights. Check source, licence, consent or other permission for data used in development, testing, fine-tuning and ongoing service delivery.
  7. Review the contract stack. Read supplier, customer, cloud, API, DPA, security, outsourcing and change-control documents together.
  8. Confirm IP and open-source position. Request code provenance, licences, notices, ownership assignments, third-party claims and output-use restrictions.
  9. Test material statements. Compare product marketing, investor materials and customer commitments against the available technical and legal evidence.
  10. Assign the deal response. Separate issues requiring price, warranty, indemnity, condition, remediation, disclosure or post-closing integration action.

How should findings affect the transaction documents?

Translate each material finding into an owner, timing and remedy. A diligence report is useful only if the SPA, investment agreement, disclosure process and integration plan reflect the issues that have been identified.

The appropriate response will depend on the transaction structure and the seller’s ability to remediate. A buyer may need targeted warranties concerning data rights, AI-related regulatory compliance, ownership, contract compliance, absence of claims or material incidents. Confirmed gaps may justify a specific indemnity, a pre-closing remediation covenant, a post-closing plan, a condition or a tailored disclosure. The drafting should not assume that a general compliance warranty captures the actual issue.

Post-closing planning is equally important where the buyer will integrate systems, move data, introduce a new group policy, change suppliers or expand the target’s use case. These changes can alter the GDPR and AI Act analysis. If an assessment is required, the timing should be addressed before the relevant processing or deployment begins. Our DPIA vs FRIA guide explains why those two assessment routes must be screened separately.

When does a separate specialist review become necessary?

A focused AI legal review should be coordinated with corporate, technical, information-security, employment and commercial due diligence when the target develops AI products, relies on proprietary datasets, makes regulated-sector decisions, uses AI in recruitment or credit processes, processes sensitive personal data, markets compliance claims, or has important dependencies on a small number of providers. The workstreams should share the same factual inventory, but each should retain its own legal questions and conclusions.

How Atrium Romanian Lawyers can assist

Atrium Romanian Lawyers can coordinate the legal workstream for AI-related due diligence in a Romanian investment, acquisition or internal reorganisation. The review can cover AI Act role and use-case screening, GDPR and data-contract questions, supplier and customer terms, intellectual property, employment and operational governance, and the translation of findings into transaction documents or an integration plan.

Client experience

AI due diligence during the acquisition of a Romanian technology company

An international investor considered acquiring a Romanian technology company that relied extensively on AI-enabled software products and third-party AI services.

During the due diligence process, the buyer requested confirmation regarding AI Act compliance, data rights, intellectual-property ownership and the target’s dependencies on external AI providers.

The review identified gaps between the target’s public marketing materials and its internal documentation, uncertainties regarding the scope of rights over certain datasets, and contractual limitations affecting the use of third-party AI services after closing.

Atrium Romanian Lawyers coordinated the legal review of the AI use cases, supplier contracts, GDPR implications and intellectual-property position. The findings were translated into targeted warranties, disclosure items and a post-closing remediation plan.

The transaction proceeded with a clearer allocation of regulatory, contractual and operational risks and with a structured roadmap for post-closing compliance measures.

This example has been anonymised and simplified for publication. The appropriate legal analysis depends on the system, data, contract structure and facts of each matter.

Frequently asked questions

Does every investment in a Romanian company need AI due diligence?

No. The scope should be proportionate to the target’s actual use of AI and the importance of that use to the transaction. A company using a limited internal tool may require a focused review. A target selling AI-enabled products, using sensitive data or making decisions affecting people may need a deeper legal and technical workstream.

Is AI due diligence the same as an AI Act compliance audit?

No. AI Act compliance is one part of the review. Transaction diligence also considers ownership, licences, customer commitments, personal data, confidentiality, technical dependencies, product claims, change control and what the buyer will need after closing. The correct scope follows the investment thesis and the target’s operating reality.

Can a seller rely on a supplier’s AI compliance statement?

Supplier information can be relevant evidence, but it does not by itself establish that the target’s own deployment is compliant. The investor should check whether the statement identifies the actual system, model, purpose, data, users, territory, contract terms and responsibilities relevant to the target’s use case.

Should a buyer ask for the target’s DPIAs?

Where the target operates AI systems involving personal data and has conducted or screened for a DPIA, the relevant material should be reviewed subject to confidentiality controls. The question is not simply whether a document exists, but whether it reflects the current processing, risks, safeguards, changes and any residual issues requiring follow-up.

Can AI findings be addressed after closing?

Sometimes. The decision depends on the nature of the issue, legal exposure, urgency, operational dependency and the buyer’s ability to control remediation. A defensible post-closing plan should identify the owner, evidence, budget, deadlines and the effect on continued use. Some issues may need to be resolved before closing or before a planned deployment.

What is the most common gap in AI diligence?

A frequent gap is that the target has a high-level AI policy or vendor contract but no reliable inventory linking systems, use cases, data, roles, evidence and decision owners. The first practical step is usually to build that factual map before drawing legal conclusions or negotiating transaction protection.
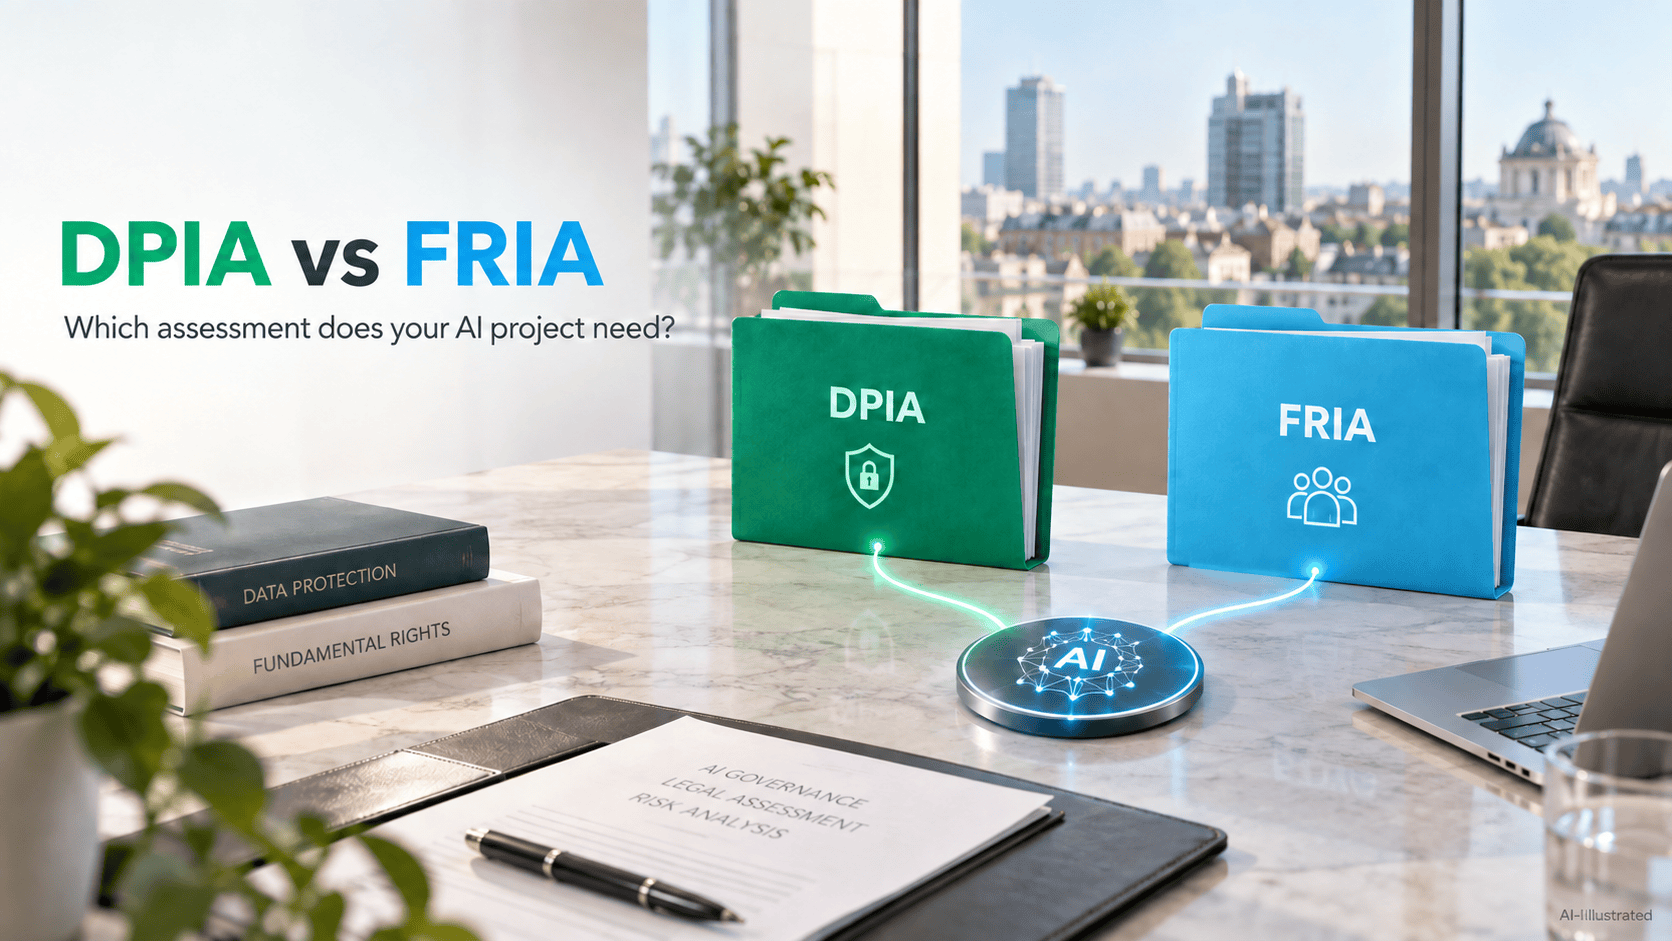
DPIA and FRIA assessment paths for an AI project in Romania

DPIA vs FRIA in Romania: Which Assessment Does Your AI Project Need?

AI governance • Romania • Assessment decisions

DPIA vs FRIA in Romania is a question of two different legal tests. A data protection impact assessment (DPIA) addresses risks arising from personal-data processing under the GDPR. A fundamental rights impact assessment (FRIA) under the AI Act applies to specified deployers of certain high-risk AI systems. Your project may require one, both, or neither mandatory assessment.

When do these obligations apply?

The GDPR assessment requirements already apply. Under the AI Act’s consolidated timetable, Chapter III Sections 1–3, including Article 27, apply to Annex III high-risk systems from 2 December 2027. The corresponding date for Article 6(1)/Annex I product systems is 2 August 2028; that does not extend Article 27 to every product system.

Article 111 contains separate transition provisions for existing systems. A project review should record when the system was placed on the market or put into service and whether subsequent design changes affect its treatment. The future FRIA timetable does not postpone GDPR duties. Source: consolidated AI Act, Articles 111 and 113.

DPIA vs FRIA: the differences that change your project

Both assessments examine potential harm to people. A DPIA is not limited to confidentiality or cybersecurity: it also examines other rights and freedoms affected by personal-data processing. FRIA addresses the impact of the specified AI deployment on fundamental rights.

Click or tap a row to reveal its practical takeaway. Keyboard users: Tab to a green label and press Enter or Space. Swipe the table sideways on a small screen.

Two assessments, separate applicability tests
Decision pointDPIA: GDPR Article 35FRIA: AI Act Article 27
Personal-data processing likely to create high risks to individuals, assessed in its context.A covered deployer using an in-scope Article 6(2)/Annex III high-risk system.
The controller, with DPO advice where a DPO is designated and relevant processor assistance.The deployer covered by Article 27.
Processing, necessity, proportionality, risks to people and safeguards.Deployment context, affected groups, risks of harm, human oversight and responses.
Before the relevant processing begins; review when risk changes.Before first use where the obligation applies; update changed or outdated elements.
Prior consultation when the Article 36 threshold is met; no universal filing requirement for every DPIA.Notify results to the market surveillance authority under Article 27(3), subject to its exception.
Shared evidence can support the assessment of the actual processing.Relevant DPIA sections may be cross-referenced or incorporated; remaining requirements still need coverage.

GDPR Articles 28, 35–36 and 39; AI Act Article 27.

When does an AI project need a DPIA?

AI use alone does not automatically trigger a DPIA. The controller must assess whether the nature, scope, context and purposes of the processing make a high risk to people likely. Article 35 expressly recognises the relevance of new technologies.

The GDPR identifies particular situations, including systematic and extensive automated evaluation underpinning decisions with legal or similarly significant effects, large-scale processing of special-category or criminal-offence data, and large-scale systematic monitoring of publicly accessible areas. Applicable supervisory-authority lists must also be checked.

For a Romanian deployment, the file should therefore address the applicable requirements and guidance of the Romanian data protection authority, ANSPDCP, alongside Article 35. Record the reasons for a negative screening conclusion too. A supplier’s description of a product as “low risk” is not an assessment of your processing.

Where required, the DPIA must describe the processing and purposes, assess necessity and proportionality, evaluate risks to individuals and specify safeguards. This is a substantive project assessment, not simply a signed template. Source: GDPR Article 35.

For the broader data-protection framework, see our guide to GDPR compliance when using AI in Romania.

Who needs a FRIA under the AI Act?

The Article 27 obligation does not cover every business using high-risk AI. It concerns Article 6(2) high-risk systems and specified categories of deployer, with an exclusion for the critical-infrastructure area in Annex III point 2.

  • Bodies governed by public law deploying qualifying systems.
  • Private entities providing public services deploying qualifying systems. This status requires analysis; it is not synonymous with every company selling services to the public.
  • Deployers of qualifying creditworthiness or credit-scoring systems for natural persons under Annex III point 5(b), which excludes systems used to detect financial fraud.
  • Deployers of qualifying life and health insurance risk-assessment or pricing systems for natural persons under Annex III point 5(c).

Classification under Article 6 must be checked first, including the conditions of any applicable exception. The exact intended purpose matters. A financial-sector tool is not automatically a creditworthiness system, and a medical product is not automatically within the Article 27 FRIA route. Source: AI Act Articles 6 and 27 and Annex III.

Explore four deployment scenarios

These hypothetical examples explain the screening logic. They assume the stated facts and do not replace an assessment of the actual system, applicable dates or transition rules.

Candidate ranking: DPIA and FRIA can diverge

A private manufacturer uses extensive automated applicant evaluation to support hiring decisions. These facts point to a DPIA requirement under Article 35(3)(a), even if a person makes the final decision. Recruitment may also fall within Annex III. However, on the assumption that the manufacturer is neither a public-law body nor a private public-service provider, its employer status alone does not trigger Article 27 FRIA.

Consumer credit: prepare for both assessments

A lender uses an in-scope high-risk system to score individuals for loan eligibility. Systematic and extensive profiling with significant consequences can trigger a DPIA. Article 27 separately covers qualifying deployers under Annex III point 5(b). Address the applicable FRIA timetable and any transition provisions, rather than assuming both duties started on the same date.

Public benefits: assess deployment and processing together

A public body uses a qualifying high-risk system to assess eligibility for essential assistance benefits. Its status and use case bring Article 27 into the analysis. The personal-data processing needs separate DPIA screening, including relevant public-task legislation and any Article 35(10) position. One completed assessment does not automatically discharge the other.

Drafting assistant: examine the actual workflow

A team drafts generic product descriptions without personal data or decisions about people. On those narrow facts, the workflow does not itself establish a DPIA or Article 27 FRIA requirement. Check account data, logs and supplier processing separately. Introducing customer records, employee evaluation or regulated decisions changes the analysis. Other duties may still apply.

Can one assessment document cover DPIA and FRIA?

A coordinated file can reduce duplicated work, provided each legal requirement remains identifiable. The consolidated Article 27(4) expressly allows relevant DPIA sections to be cross-referenced or incorporated into FRIA where they already meet the corresponding obligations.

Start with a shared description of the system, purposes, data flows, affected people and safeguards. Then keep a requirement map showing which sections satisfy GDPR Article 35 and which satisfy AI Act Article 27. Identify gaps rather than renaming a DPIA “FRIA”. Source: AI Act Article 27(4)–(5).

As a practical drafting approach, include a separate deployment chapter addressing who may be affected beyond the immediate users, how mistakes influence access to opportunities or services, who can intervene, and how complaints lead to corrective action. Avoid treating GDPR as only a privacy checklist: the DPIA itself must consider risks to rights and freedoms.

What the FRIA needs to address

Article 27 requires the deployment process and intended use, duration and frequency, affected people and groups, specific risks of harm, implementation of human oversight, and measures if risks materialise, including governance and complaint mechanisms. Reusing a supplier assessment in similar cases is permitted, but the deployer must check its fit and update changed or outdated elements. Source: AI Act Article 27(1)–(2).

Who prepares, reviews and owns the decision?

The controller remains responsible for the DPIA; the covered deployer remains responsible for FRIA. A consultant, DPO or supplier can contribute without taking over the organisation’s statutory role.

For the DPIA, seek the designated DPO’s advice and preserve their independent advisory and monitoring function. Obtain relevant processor assistance. For the deployment review, involve the business owner, technical team and people responsible for oversight and complaints. A useful internal decision records outstanding conditions, the person accountable for each safeguard and the circumstances requiring a fresh review. Source: GDPR Articles 28(3)(f), 35(2) and 39; AI Act Article 27.

Contractual cooperation should cover the evidence you need to assess the deployment. Our AI vendor contracts guide addresses information rights, changes and supplier responsibilities.

Must the assessment be sent to an authority?

A DPIA and a FRIA follow different authority procedures. Under GDPR Article 36, prior consultation is required where high residual risk remains that cannot be sufficiently mitigated. There is no general GDPR obligation to submit every DPIA for approval.

Article 27(3) provides for notification of FRIA results to the market surveillance authority using the relevant template, subject to the Article 46(1) exception. That notification is not the GDPR prior-consultation procedure and should not be described as automatic permission to deploy. Confirm the competent authority and operational submission arrangements for the specific deployment. GDPR Article 36; AI Act Article 27(3).

A practical assessment file before deployment

  1. Define the use case. Identify the system, version, intended purpose, users, affected people and decisions it informs.
  2. Map roles separately. Record GDPR controller/processor roles and the relevant AI Act roles.
  3. Screen the legal route. Check prohibited practices, AI classification, DPIA triggers and Article 27 deployer coverage.
  4. Record timing. Distinguish existing GDPR duties from future AI Act requirements and applicable transition provisions.
  5. Collect evidence. Obtain data-flow information, supplier instructions, meaningful performance limitations, oversight arrangements and relevant testing.
  6. Assess harms and safeguards. Describe how the actual deployment may affect people and how controls reduce those risks.
  7. Map shared sections. Make each DPIA and FRIA requirement traceable, retaining any necessary separate analysis.
  8. Resolve escalation. Identify prior consultation, notification, unresolved risks and conditions preventing launch.
  9. Assign review triggers. Consider changes in purpose, model, data, affected groups or decision authority, and evidence from incidents or complaints.

How Atrium Romanian Lawyers Assisted an International Manufacturing Group

Anonymised client matter. The description below omits identifying information and focuses on the legal work performed.

Questions examined

  • Whether the candidate-data processing required a DPIA;
  • Whether the use of the system could trigger a FRIA under the AI Act;
  • What human-oversight and documentation measures were needed before implementation.

Legal analysis

Our review of the recruitment process identified extensive automated evaluations of candidates with a significant impact on access to employment opportunities. The company therefore decided to complete a DPIA before implementation.

We also carried out a separate analysis of the system’s classification under the AI Act, including the organisation’s status and the obligations applicable to the deployer. The review confirmed that the DPIA and any FRIA analysis had to be treated separately because their legal triggers differ.

Measures adopted

  • Documentation of the decision logic and system limitations;
  • Mandatory stages of human verification;
  • Internal procedures for challenging results and handling complaints;
  • Updated contractual documentation and AI-governance workflows.

Practical result

Following the project, the company was able to continue the implementation on the basis of stronger documentation concerning compliance and risk management.

A focused consultation can clarify which assessment route applies and what your team needs before making deployment commitments.

Frequently asked questions

Does every AI project need both a DPIA and a FRIA?

No. Screen personal-data processing under GDPR Article 35 and, separately, the system and deployer under AI Act Article 27. One assessment may be mandatory while the other is not. A negative screening result does not remove other applicable legal obligations.

Does human review remove the need for a DPIA?

Not automatically. Article 35 has its own risk test, and its automated-evaluation category is not confined to solely automated decisions. Genuine human oversight can affect risks and safeguards, but a human signature does not by itself settle DPIA applicability.

Does a private employer need a statutory FRIA for recruitment AI?

Not solely because it is an employer using high-risk recruitment AI. Article 27 covers specified deployers and uses. Check whether the organisation is a public-law body or private public-service provider, while independently assessing its GDPR and other AI Act obligations.

Can we rely on the supplier’s impact assessment?

Supplier evidence can support the work, and Article 27 permits reliance on existing assessments in similar cases. The organisation still needs to check whether the document addresses its actual deployment, affected groups, safeguards and applicable obligations. A generic assurance is insufficient evidence of that fit.

Can we wait until the FRIA application date to conduct a DPIA?

No, if GDPR already requires a DPIA for the proposed processing. The DPIA must precede that processing. The AI Act timetable and transition provisions must be analysed separately and do not suspend GDPR requirements.

Does completing an assessment authorise the project?

No. An assessment documents analysis and safeguards; it does not supply a missing legal basis, legalise prohibited AI or override unresolved legal restrictions. Complete any required consultation or notification procedure and resolve conditions that prevent lawful deployment.

Corporate data breach response centre managing a GDPR incident in Romania

GDPR Data Breach in Romania: 72-Hour Guide

A GDPR data breach in Romania creates an immediate legal decision window. The company must contain the incident, determine whether personal data were compromised, assess the risk to individuals and decide whether the Romanian supervisory authority, the ANSPDCP, must be notified within 72 hours.

GDPR data breach response and personal data security in Romania

What companies should know immediately:

  • The 72-hour period runs from the controller’s awareness of the breach, not necessarily from the moment the incident first occurred.
  • Every personal data breach must be documented, even when notification is not required.
  • The ANSPDCP must be notified unless the breach is unlikely to create a risk to individuals’ rights and freedoms.
  • Affected individuals must also be informed without undue delay when the breach is likely to create a high risk.
  • An incomplete investigation does not justify silence. GDPR permits information to be submitted in phases.

This guide is designed for Romanian companies, foreign investors, directors, compliance teams and data protection officers responding to an actual or suspected incident. It should be used together with an incident-specific legal and technical assessment. For preventive support and breach response, see our data protection services in Romania.

What qualifies as a personal data breach?

Article 4(12) of the General Data Protection Regulation defines a personal data breach as a security breach leading to accidental or unlawful destruction, loss, alteration, unauthorised disclosure of or access to personal data. The concept is wider than a cyberattack and covers confidentiality, integrity and availability incidents.

Breach typeWhat it meansCommon exampleImmediate check
ConfidentialityPersonal data are accessed or disclosed without authorisation.An email with customer files is sent to the wrong recipient, credentials are stolen or an attacker exfiltrates a database.Who received or accessed the data, and can further access be stopped?
IntegrityPersonal data are altered without authorisation or by accident.Payroll details are changed, records are corrupted or an unauthorised user modifies a customer account.Which records changed, can the original data be restored, and were decisions made using incorrect data?
AvailabilityPersonal data become unavailable or are destroyed.Ransomware encrypts files, a database is deleted or a lost device contains the only copy of records.Are reliable backups available, how long will services be disrupted, and could the loss harm individuals?

A security event that does not involve personal data is not a personal data breach under GDPR. Conversely, a small incident can still be a breach. Under the data protection rules applicable in Romania, the number of affected people matters, but so do the sensitivity of the data, the ease of identification, the possible consequences and the vulnerability of the people concerned.

When does the 72-hour notification period start?

Article 33 requires notification without undue delay and, where feasible, no later than 72 hours after the controller becomes aware of the breach. According to the EDPB breach-notification guidelines, awareness exists when the controller has a reasonable degree of certainty that a security incident occurred and led to personal data being compromised.

A brief initial investigation may be necessary to determine whether personal data were actually affected. That does not permit an organisation to delay investigation or postpone escalation. Once there is reasonable certainty, the clock runs even if the full cause, exact number of records or final consequences are still being investigated.

72-hour incident clock
From awareness to notification

Select a stage to see the priority. The timetable is operational guidance, not a replacement for immediate action.

Confirm awareness

Record when the controller first reached a reasonable degree of certainty that personal data had been compromised. Preserve the facts supporting that timestamp.

Do not wait for a final forensic report before making the legal notification decision. Article 33 expressly permits phased notification when all information cannot be provided at the same time.

Must every breach be notified to the ANSPDCP?

No. Every breach must be recorded internally, but not every breach must be reported to the authority. The controller must assess the likely impact on the rights and freedoms of natural persons. The result falls into one of three practical levels.

Notification decision matrix
Choose the response level

Select a risk level to see the corresponding GDPR response. The conclusion must be supported by documented facts.

Document internally

If the breach is unlikely to result in a risk to individuals, authority notification is not required. The breach, assessment, effects and remedial action must still be recorded.

Assessment resultRequired actionTypical considerations
Unlikely to create riskDocument the breach and the reasons for not notifying.Strong effective safeguards, limited data, verified recovery, no realistic adverse effect and reliable containment.
Likely to create riskNotify the competent supervisory authority without undue delay and, where feasible, within 72 hours.Possible identity theft, fraud, loss of confidentiality, discrimination, financial loss, reputational harm or loss of control over data.
Likely to create high riskNotify the authority and communicate with affected individuals without undue delay, unless an Article 34 exception applies.Special-category data, credentials or financial data, vulnerable people, large-scale exposure, easy identification or serious likely consequences.

Risk is not determined by a single formula. The company should consider the type of breach, nature and volume of data, identifiability, severity and likelihood of consequences, number and characteristics of affected people, and the effectiveness of safeguards such as encryption. The EDPB’s practical breach examples are useful benchmarks, but the actual incident must be assessed on its own facts.

What must an ANSPDCP notification contain?

Article 33(3) establishes the minimum information. The ANSPDCP’s current online notification form requests additional operational details that allow the authority to understand the incident and the controller’s response.

Notification fieldWhat the company should prepare
Nature of the breachA concise incident summary, whether confidentiality, integrity or availability was affected, and the relevant systems and processing operations.
People and recordsCategories and approximate number of affected data subjects, plus categories and approximate number of personal data records.
Contact pointName and contact details of the DPO or another person able to provide further information.
Likely consequencesThe realistic adverse effects for individuals, including how they could occur and which groups face the greatest exposure.
MeasuresContainment and remediation already performed, further measures proposed, and actions intended to mitigate adverse effects.
TimelineIncident date and time where known, detection, awareness, response milestones and reasons for any notification made after 72 hours.
Additional contextProcessors involved, security measures, cross-border aspects, other authorities notified and whether the filing is initial or supplemental.

If exact figures are not yet available, provide reasonable estimates and state that the investigation continues. Under Article 33(4), missing information may be supplied in phases without undue further delay. If the filing occurs after 72 hours, it must include reasons for the delay.

How is a breach notified in Romania?

The ANSPDCP maintains a dedicated personal data breach notification page with access to its online form. Before submission, the company should identify the correct controller, confirm whether the incident also affects other group entities or joint controllers, and determine whether the ANSPDCP is the competent or lead supervisory authority for any cross-border processing.

The notification should be consistent with the internal breach register, technical evidence, communications plan and any supplemental filing. A company should not understate confirmed facts, speculate beyond the evidence or present an incomplete notification as final.

Enforcement point: the ANSPDCP has publicly reported sanctions for failure to notify a personal data breach within the 72-hour period. Breach-notification obligations under Articles 33 and 34 also fall within the GDPR administrative-fine tier of up to EUR 10 million or, for an undertaking, up to 2% of total worldwide annual turnover for the preceding financial year, whichever is higher. The actual measure depends on the Article 83 assessment and the circumstances of the case.

Who should be involved in the response?

A data breach cannot be handled by IT alone. The legal assessment depends on verified technical facts, while technical containment must preserve evidence and avoid creating inconsistent records. A small decision team should be activated immediately, with clear authority and one incident chronology.

Response team
Four connected workstreams

Select a workstream to see its principal responsibility. All teams should work from the same verified timeline.

Security and IT

Contain the incident, preserve logs and forensic evidence, confirm affected systems and data, remove persistence, restore safely and record every material action.

  • Security and IT: containment, forensic preservation, affected-system analysis, eradication, recovery and evidence of technical safeguards.
  • DPO and legal counsel: awareness timestamp, controller or processor status, risk assessment, authority competence, notification drafting and privilege strategy where applicable.
  • Management and communications: decision authority, resources, operational continuity, messaging and escalation to insurers or relevant corporate bodies.
  • Processors and vendors: incident facts, contractual notification, audit cooperation, subprocessor information and coordinated remedial action.

What is the difference between a controller and a processor?

The controller decides why and how personal data are processed and carries the Article 33 duty to notify the competent supervisory authority. A processor must notify the controller without undue delay after becoming aware of a personal data breach. GDPR does not give processors a separate 72-hour period for notifying the controller.

Data processing agreements should therefore establish an immediate escalation channel, minimum incident information, continuous updates, preservation duties and cooperation with notifications and communications. A processor’s delayed or incomplete report does not remove the controller’s obligation once the controller becomes aware.

RolePrimary breach dutyContractual control
ControllerAssess risk, document every breach, notify the competent authority where required and communicate with individuals where high risk is likely.Maintain response governance and require processors to provide prompt, usable incident information.
ProcessorNotify the controller without undue delay and assist with the controller’s Article 32–36 obligations.Define rapid reporting, evidence preservation, subprocessor escalation, investigation access and update frequency.
Joint controllersAllocate responsibilities transparently, while each remains accountable for the GDPR obligations applicable to it.Agree in advance who leads investigation, authority contact and data-subject communication.

Vendor and technology contracts should be reviewed before an incident occurs. Our IT law services in Romania cover data-processing terms, security obligations, audit rights and incident-response clauses.

When must affected individuals be informed?

Under Article 34, the controller must communicate the breach to affected individuals without undue delay when it is likely to result in a high risk to their rights and freedoms. This obligation is separate from the 72-hour authority-notification rule. The communication must use clear and plain language and explain the nature of the breach, the contact point, likely consequences and measures taken or proposed.

Communication is not required when one of the Article 34(3) conditions applies:

  • appropriate protection measures applied to the affected data and made them unintelligible to unauthorised persons, such as effective encryption;
  • subsequent measures ensure that the high risk is no longer likely to materialise; or
  • individual communication would involve disproportionate effort, in which case a public communication or similarly effective measure is required.

The message should help people protect themselves. Depending on the incident, practical steps may include changing credentials, enabling multi-factor authentication, contacting a bank, monitoring accounts, watching for targeted phishing or using a dedicated support contact. Avoid minimising the event or overwhelming recipients with technical detail.

How should breach risk be assessed?

The legal threshold concerns risk to people, not only damage to the company. Business interruption, contractual liability and reputational harm matter to the response, but they do not replace the individual-rights analysis required by Articles 33 and 34.

Breach risk map
Where can harm materialise?

Select a risk area to review typical consequences. More than one area may apply to the same incident.

Identity fraud and impersonation

Identification data, credentials, signatures or financial information may enable account takeover, fraudulent transactions or convincing social-engineering attacks.

High-risk indicators include sensitive or criminal-offence data, authentication credentials, detailed financial or identity information, data concerning children or other vulnerable people, large-scale exposure, malicious exfiltration, weak safeguards and consequences that are difficult for individuals to reverse. Effective encryption, rapid verified retrieval from a trusted recipient and prompt credential revocation may reduce risk, but each control must be tested against the facts.

What evidence and documentation should be preserved?

Article 33(5) requires the controller to document every personal data breach, including the facts, effects and remedial action. The record must allow the supervisory authority to verify compliance. A defensible incident file should include:

  • the original alert, detection data and a precise incident chronology;
  • the awareness timestamp and the facts supporting it;
  • affected systems, processing activities, data categories, people and record estimates;
  • logs, forensic images, access records, emails, vendor reports and chain-of-custody information where relevant;
  • containment, eradication, recovery and mitigation actions;
  • the risk and high-risk assessments, including reasons and assumptions;
  • the decision to notify or not notify, approvals and any delay explanation;
  • copies of the initial and supplemental ANSPDCP filings;
  • data-subject communications or the documented Article 34 exception; and
  • post-incident findings, corrective actions and responsibility for completion.

Records should distinguish confirmed facts from estimates and hypotheses. The company should also consider cybersecurity, contractual and insurance requirements, DORA and other sector-specific reporting duties, and criminal-law reporting duties. These may use different thresholds and deadlines from GDPR.

A practical 72-hour response checklist

  1. Activate the incident team. Establish one decision lead, secure communications and a contemporaneous chronology.
  2. Contain without destroying evidence. Isolate affected resources, revoke compromised access and preserve logs and forensic material.
  3. Confirm whether personal data are involved. Identify the controller, processor, systems, processing activities and data flows.
  4. Record the awareness timestamp. Explain when reasonable certainty was reached and what facts supported it.
  5. Map the scope. Identify data categories, affected people, approximate record volumes, jurisdictions and vulnerable groups.
  6. Assess risk to individuals. Analyse likelihood, severity, safeguards, realistic misuse and reversibility of harm.
  7. Decide on authority notification. Notify unless the breach is unlikely to create risk. Use phased notification if necessary.
  8. Assess high risk separately. Decide whether individuals must be informed and prepare clear protective guidance.
  9. Coordinate other duties. Review processors, insurers, contractual partners, cybersecurity rules and sector regulators.
  10. Continue and close the response. Supplement filings, verify recovery, complete remediation and retain the breach record.

For a broader preventive review, use our GDPR compliance checklist for Romanian companies. Even though the checklist was published earlier, the core governance controls remain relevant and should be checked against current processing and security practices.

Frequently asked questions

Does the 72-hour period start when IT sees the first suspicious alert?

Not necessarily. The EDPB treats a controller as aware when it has a reasonable degree of certainty that a security incident occurred and compromised personal data. A short initial investigation may establish whether a breach occurred, but it must begin promptly and cannot be used to delay awareness artificially.

Must every ransomware incident be notified to the ANSPDCP?

Not automatically, but ransomware often creates availability, integrity and possibly confidentiality risks. The controller must determine whether personal data were affected, whether exfiltration or unauthorised access occurred, whether reliable backups exist and what consequences are likely for individuals. The conclusion and supporting facts must be documented.

Is an email sent to the wrong recipient a reportable breach?

It is normally a confidentiality breach if personal data were disclosed without authorisation. Whether ANSPDCP notification is required depends on the risk assessment, including the data involved, recipient, ability to retrieve or delete the message, evidence of access and possible consequences. The incident must still be recorded internally.

Can a company notify before the investigation is complete?

Yes. Article 33 permits phased notification when all required information cannot be provided at the same time. The initial notification should contain the available facts and make clear what remains under investigation. Additional information must be supplied without undue further delay.

Does a processor notify the ANSPDCP directly?

The processor’s express Article 33 duty is to notify the controller without undue delay. The controller assesses and makes the supervisory-authority notification. Separate duties may arise from the processor’s own role in other processing, contractual arrangements, cross-border circumstances or sector-specific law.

Must affected people always be informed?

No. Direct communication is required when the breach is likely to result in a high risk, unless an Article 34(3) exception applies. Authority notification uses the lower threshold of likely risk. A breach may therefore require ANSPDCP notification without requiring direct communication to individuals.

What happens if the 72-hour deadline is missed?

The company should notify without further delay and explain why the filing is late. A missed deadline does not remove the notification obligation. The authority may consider the delay, cooperation, mitigation, severity and other Article 83 factors when deciding on corrective measures or a fine.

Need urgent advice on a GDPR data breach in Romania?

We help companies assess notification thresholds, prepare ANSPDCP filings, coordinate processor responses and draft communications to affected individuals.

Book a consultation

Legal disclaimer: This article provides general information and does not constitute legal advice. The applicable response depends on the facts, the company’s role, the data and individuals affected, the competent authority and any sector-specific obligations. Obtain advice for the specific incident.

AI Notice: AI-assisted content, reviewed and approved by a qualified Romanian lawyer.

Romanian business professional reviewing GDPR compliance checklist on laptop in Bucharest office

GDPR Compliance Checklist for Romanian Companies 2025

Play

GDPR Compliance Checklist for Romanian Companies

What crucial step could protect your business from devastating fines while building customer trust?

Many organizations underestimate how Europe’s strict data protection laws apply to their operations.

While GDPR penalties can reach €20 million or 4% of global revenue, Romanian enforcement authorities have imposed fines ranging from €3,000 to €130,000 for violations, demonstrating that penalties scale with the severity of breaches and organizational size.

GDPR compliance checklist for Romanian companies

Romania’s evolving digital economy demands proactive measures to align with rigorous privacy standards.

Legal experts emphasize that proper adherence involves more than basic policy updates—it requires systematic data governance.

Companies must address consent protocols, breach response plans, and cross-border data flows to avoid regulatory scrutiny.

Specialized legal guidance helps businesses transform compliance into strategic advantages.

Firms adopting privacy-first approaches often see improved client relationships and operational resilience.

Those delaying action risk not only financial consequences but also long-term reputational damage in competitive markets.

For tailored strategies meeting international standards, contact our data protection lawyers in Bucharest.

Our team of legal professionals provide actionable frameworks to navigate complex requirements while prioritizing business growth.

Key Takeaways

  • Data protection laws apply regardless of a company’s physical location if EU resident information is processed,
  • Penalties can reach €20 million or 4% of global revenue, emphasizing the need for preventive measures,
  • Building customer trust through transparent data practices creates market differentiation,
  • Legal experts offer customized solutions to align business operations with regulatory demands,
  • Compliance involves continuous monitoring, not just one-time adjustments.

Understanding GDPR and Its Impact on Romanian Businesses

How can organizations in Romania turn regulatory demands into strategic opportunities?

The General Data Protection Regulation (GDPR) reshapes how businesses manage information, particularly for entities handling EU residents’ data.

Its extraterritorial scope means even non-EU-based firms must adhere to strict standards when processing personal details of European citizens.

Core Regulatory Foundations

The regulation establishes six foundational principles for data handling, plus an overarching accountability principle.

These mandate that organizations:

  • Process information lawfully and transparently,
  • Collect only necessary data for specific purposes,
  • Maintain accuracy and limit storage durations.

Such requirements demand technical safeguards like encryption and operational protocols for accountability.

Privacy-by-design methodologies ensure protections are embedded in all systems.

Strategic Advantages for Local Entities

Adhering to these standards transforms obligations into opportunities.

Firms prioritizing data protection report:

  • Enhanced client confidence through transparent practices,
  • Reduced breach-related costs and operational disruptions,
  • Differentiation in markets where privacy concerns influence decisions.

For tailored strategies aligning Romanian operations with these regulations, consult our team of Romanian Lawyers.

Proactive adaptation not only mitigates risks but positions businesses as trustworthy data stewards.

Exploring Key GDPR Roles and Terminology

Who holds ultimate accountability in data governance frameworks?

Clarifying responsibilities under privacy regulations helps organizations establish clear operational boundaries.

Three critical roles form the foundation of proper data management practices.

data protection officer

Data Controllers, Processors, and Data Subjects

Data controllers determine why and how personal information is handled.

They bear legal responsibility for compliance across all processing activities.

Third-party processors execute tasks under controller directives but must independently meet security standards.

Individuals whose data is collected, known as data subjects, retain rights to access or delete their information.

Organizations must implement systems to honor these requests efficiently.

The Essential Role of the Data Protection Officer (DPO)

A data protection officer oversees compliance strategies and acts as the regulatory liaison.

This role is mandatory for entities processing sensitive data or conducting large-scale monitoring.

Under Romanian Law 190/2018, organizations processing national identification numbers (CNP) based on legitimate interest must also appoint a DPO, even if they don’t meet the standard GDPR thresholds.

This additional requirement reflects Romania’s enhanced protection for sensitive national identifiers.

Romanian businesses uncertain about role allocations should consult office@theromanianlawyers.com.

Proper classification prevents overlapping liabilities and ensures alignment with cross-border standards.

Conducting a Comprehensive Data Audit and Mapping

Organizations handling personal information must first establish clarity in their data ecosystems.

A systematic audit reveals how data flows through operations, exposing vulnerabilities while ensuring alignment with legal obligations.

This foundational step transforms raw information into actionable insights for risk management.

data audit and mapping

Identifying What Personal Data You Collect

Begin by cataloging every category of personal data your organization processes.

Common examples include:

  • Contact details (names, email addresses).
  • Digital identifiers (IP addresses, device information).
  • Sensitive records (financial data, health information).

Document each data point’s purpose, collection method, and retention timeline.

Assess whether processing activities rely on valid legal grounds like contractual necessity or explicit consent.

Storage locations demand equal scrutiny—identify physical servers, cloud platforms, and third-party repositories holding sensitive materials.

Access controls form another critical audit component.

Map which employees or systems interact with personal data and verify authorization protocols.

This process highlights potential exposure points while streamlining responses to information requests.

Romanian entities seeking structured frameworks for these assessments may contact our data protection legal specialists.

Expert guidance ensures audits meet regulatory expectations while supporting operational efficiency.

GDPR Compliance Checklist for Romanian Companies

Businesses handling EU data face operational complexity when aligning processes with privacy standards.

Structured frameworks simplify adherence while minimizing risks of non-conformance.

Effective strategies combine procedural clarity with technological safeguards to meet evolving requirements.

data protection checklist steps

Actionable Protocols for Information Security

Organizations should prioritize these critical measures:

Action ItemResponsible PartyDeadline
Complete data flow mappingIT & Legal Teams30 Days
Implement encryption protocolsSecurity Department45 Days
Update third-party contractsCompliance Officer60 Days

Consent Management Best Practices

Valid authorization requires unticked checkboxes and separate permissions for distinct processing purposes.

Confirmation emails enhance verification, while centralized logging systems track user agreements with timestamps and purpose details.

Organizations must honor withdrawal requests without undue delay and provide confirmation within one month, as required by GDPR Article 12(3).

Automated systems should flag outdated records immediately upon withdrawal, ensuring ongoing alignment with transparency obligations and ceasing processing activities promptly.

Regular audits verify adherence to storage limitation principles and access controls.

Local enterprises seeking customized frameworks may contact office@theromanianlawyers.com.

Specialized guidance helps establish resilient processes that satisfy regulatory expectations while supporting operational scalability.

Ensuring Website Security and Transparent Privacy Policies

How do modern businesses balance robust security with user transparency?

Websites storing personal information require layered defenses against cyber threats.

Organizations must adopt technical safeguards while clearly communicating data handling practices to users.

website security and privacy policies

Implementing SSL, Strong Passwords, and Anti-Virus Measures

HTTPS encryption via SSL certificates forms the first line of defense.

Multi-factor authentication and complex passwords prevent unauthorized account access.

Regular vulnerability scans and firewall updates address emerging threats.

Advanced protections include:

  • Content Delivery Networks (CDNs) to mitigate DDoS attacks,
  • Intrusion detection systems monitoring server activity,
  • Automated backups stored in geographically separate locations.

Designing Clear and Accessible Privacy Notices

Privacy policies must explain data collection purposes in plain language.

Every page should feature a visible link to these documents. Essential disclosures include:

  • Types of information gathered (contact details, device data)
  • Legal basis for processing activities
  • Third-party data sharing arrangements

Entities developing their online platforms should consult office@theromanianlawyers.com for policy reviews.

Proper alignment with privacy standards builds credibility while reducing legal exposure.

Managing Third-Party Vendors and International Data Transfers

How can businesses ensure their partners meet strict data protection standards?

Organizations relying on external vendors must verify their adherence to privacy regulations.

This requires thorough evaluations and contractual safeguards to maintain accountability across supply chains.

Evaluating Vendor Requirements and Contracts

Entities handling personal information must catalog all service providers processing data.

This includes cloud platforms, payment systems, and marketing tools.

Assessments should examine vendors’ security certifications, breach response plans, and documentation of regulatory alignment.

Legally binding agreements define responsibilities between controllers and processors.

These contracts specify permitted activities, retention timelines, and security protocols.

Subcontractor arrangements require explicit approval to maintain oversight.

RequirementActionMechanism
Vendor AccountabilityReview security auditsAnnual assessments
Data TransfersImplement SCCsContractual clauses
Risk MitigationConduct impact analysesTransfer evaluations

Cross-border data flows demand additional precautions.

Companies must confirm whether recipient countries have EU adequacy status.

For other regions, standardized contractual clauses or binding corporate rules become mandatory safeguards.

Romanian enterprises navigating these complexities should seek specialized Romanian Lawyer.

Proactive vendor management frameworks prevent regulatory violations while fostering trust with European partners.

Contact office@theromanianlawyers.com for tailored strategies addressing cross-border operational challenges.

Preparing for Data Breaches and Facilitating Data Subject Rights

What separates resilient organizations from vulnerable ones when cyber threats strike?

Proactive preparation for security incidents and efficient handling of individual rights form the backbone of modern data governance.

Organizations must balance rapid response capabilities with systematic processes to address user inquiries.

Developing a Robust Breach Response Plan

Effective incident management requires predefined protocols.

Immediate detection mechanisms trigger containment procedures within one hour of identifying unauthorized data access.

Forensic teams analyze breach scope while legal advisors determine notification obligations to authorities within 72 hours.

Regular simulation exercises test communication channels between IT, legal, and PR departments.

Documentation templates for breach reports ensure regulatory requirements are met without delays.

Continuous monitoring systems flag unusual activity patterns to prevent escalation.

Streamlining Data Subject Access Requests

Individuals increasingly exercise their right to review or delete personal information.

Centralized portals allow users to submit requests through secure authentication methods.

Automated workflows verify identities and route inquiries to appropriate teams within 24 hours.

Response templates maintain consistency while adhering to legal timelines.

Secure delivery channels protect sensitive information during transmission.

Audit trails demonstrate compliance with access rights obligations during regulatory inspections.

Entities requiring customized frameworks for incident management or user rights processes should contact office@theromanianlawyers.com.

Structured approaches transform regulatory demands into operational strengths while maintaining stakeholder trust.

FAQ

When must Romanian businesses appoint a data protection officer?

Organizations must designate a data protection officer if they systematically monitor individuals on a large scale or process sensitive categories like health records.

Public authorities in Romania also require this role regardless of data volume.

How long can companies retain customer information under EU regulations?

Storage periods must align with the original purpose for collection.

For example, transaction records may be kept for tax compliance periods specified by ANAF (Romania’s tax authority), while marketing contact lists require periodic reviews for relevance.

What technical safeguards are mandatory for website security?

Essential measures include SSL encryption, multi-factor authentication, regular penetration testing, and documented patch management processes.

Organizations should implement security measures proportionate to the risk level of data processing, following GDPR Article 32 requirements for appropriate technical and organizational measures.

Are international cloud providers like AWS or Microsoft Azure GDPR-compliant for Romanian data?

Providers operating under EU-approved mechanisms like Standard Contractual Clauses (SCCs) or binding corporate rules generally meet requirements.

However, companies must verify current certifications and update Data Processing Agreements (DPAs) annually.

What penalties apply for violating data subject rights in Romania?

The National Supervisory Authority for Personal Data Processing (ANSPDCP) can impose fines up to €20 million or 4% of global turnover.

Recent enforcement actions targeted improper consent practices and delayed breach notifications.

How should organizations handle data access requests from employees?

Businesses must respond within 30 days, providing free electronic copies of records.

Implement automated DSAR workflows in platforms like Microsoft 365 or specialized tools such as OneTrust to track and fulfill requests efficiently.