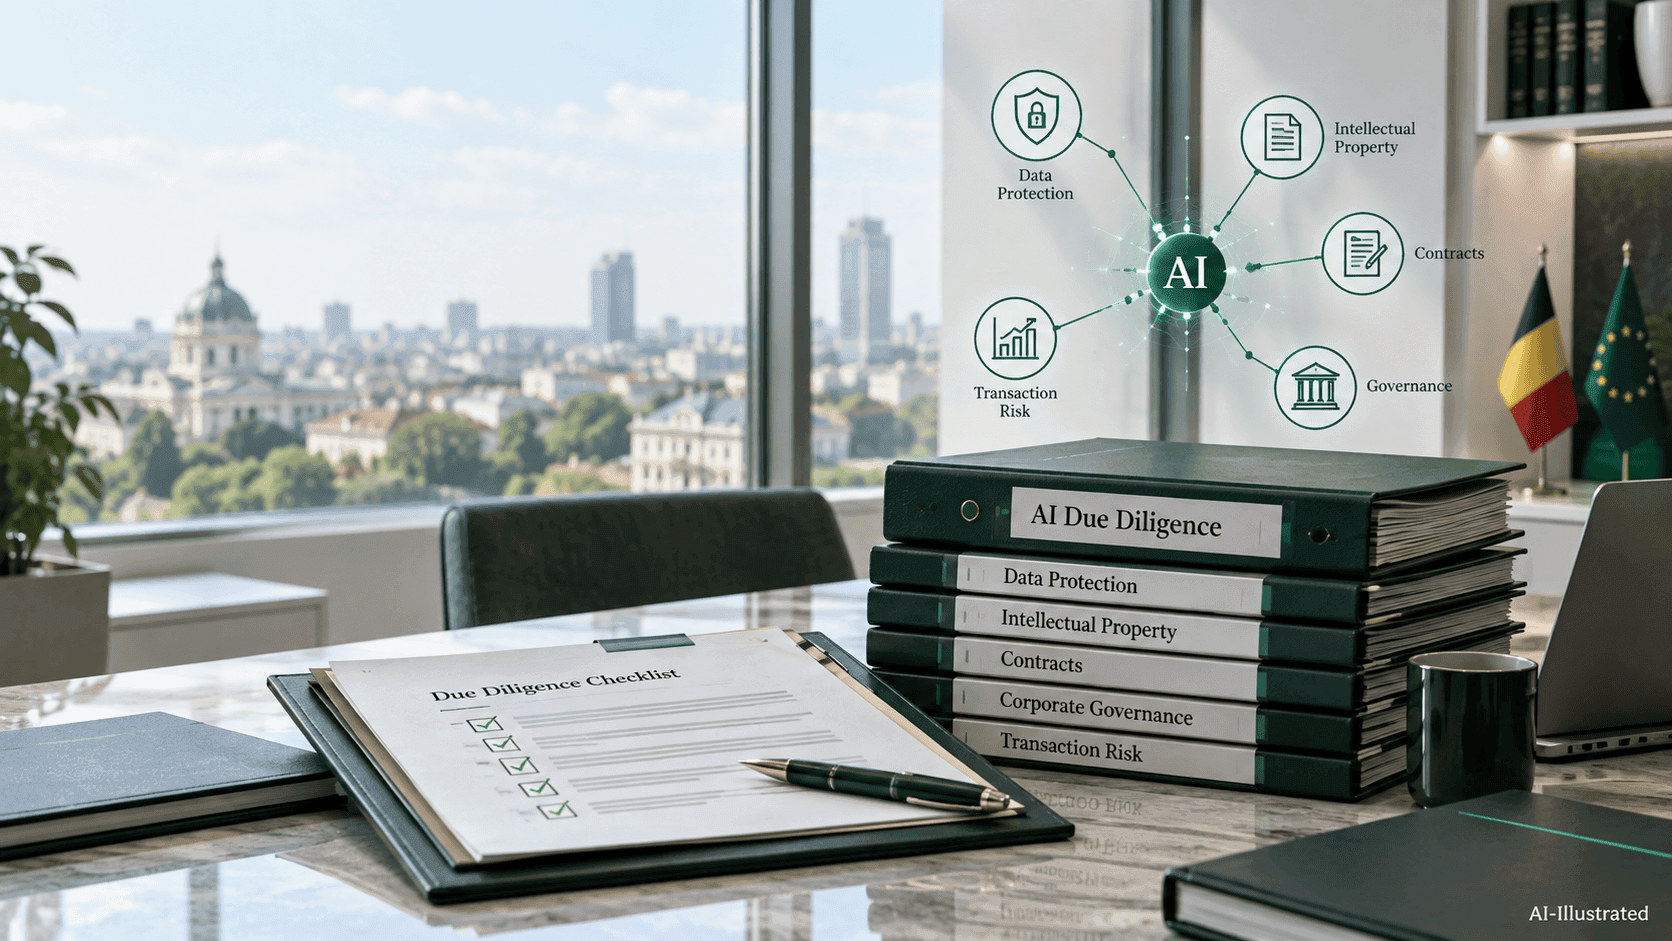
AI due diligence checklist for foreign investors assessing a Romanian company

AI Due Diligence in Romania: What Foreign Investors Should Check

Foreign investment • AI governance • Romania

AI due diligence in Romania asks whether a target company’s AI use, data, contracts and public claims support the investment case. It is not a technical demonstration of a model and it is not a generic AI policy review. For a buyer, investor or lender, the question is whether the target has identified the systems it uses, can lawfully operate them, owns or can use the assets it relies on, and has a credible plan for the risks that will remain after closing.

What is AI due diligence in a Romanian transaction?

AI due diligence is a transaction-focused legal and commercial review. It identifies whether the target’s use of AI creates liabilities, restrictions, missing rights or implementation costs that could affect price, risk allocation or post-closing operations.

For a Romanian target, the review should cover the target’s Romanian operations and any AI outputs used in the European Union. The EU AI Act is directly applicable across the EU and operates alongside the GDPR where personal data is processed. A seller’s statement that it uses only a third-party AI tool does not end the inquiry: the target may still be a deployer, customer, controller, employer or regulated business with its own duties.

This guide has a different purpose from our analysis of AI vendor contracts in Romania, which focuses on the agreement with a supplier, and from DPIA vs FRIA in Romania, which focuses on assessment triggers for a deployment. Here, the investor is deciding what must be verified before, at and after a deal.

Start with the target’s actual AI footprint

Do not begin with a broad question such as “Does the company use AI?” Ask what system or model is used, for which decision, with which data, by whom, and whether the target sells, deploys, develops, fine-tunes or merely accesses the tool.

A useful data-room request separates customer-facing products from internal tools. It should identify models, APIs, software providers, hosting and cloud dependencies, integrations, datasets, prompts or knowledge bases, material outputs, users and the decisions influenced by each use case. The inventory should also record planned products or features that have not yet launched but are material to the investment thesis.

Deal-side navigator

Select a deal question to see the first evidence to request

Click or tap a card. Keyboard users can Tab to a card and press Enter or Space. Each selection stays visible until you choose another one.

Business model and footprint

Request a system inventory, product descriptions, roadmaps, supplier contracts, architecture summary and evidence of the target’s material AI claims. Compare marketing language with the technology and operating model actually in use.

Which legal and commercial issues should an investor test?

Click or tap a row to highlight the diligence takeaway. On a small screen, swipe the table sideways.

AI due diligence matrix for a Romanian target
Review areaWhat to testPossible deal response
Whether the target’s product, sales material and internal inventory describe the same systems, functions, limits and dependencies.Correct the diligence scope, ask for technical confirmation and qualify representations that are broader than the evidence.
Whether a use case may be prohibited, high-risk, subject to transparency rules or linked to a general-purpose AI model supply chain.Obtain a classification record, identify compliance timing and budget for any remediation or implementation work.
Data flows, controller/processor roles, legal bases, Article 22 issues, DPIA screening, security measures and cross-border transfers.Require a privacy remediation plan, review the DPA and test whether the target can continue the relevant processing after closing.
Whether datasets, prompts, files or customer information may lawfully be used for development, fine-tuning, testing or supplier improvement.Limit or stop impermissible use, obtain consents or contractual permissions where appropriate, and reserve a specific risk allocation.
Ownership and licences for software, open-source components, models, training materials, brand assets, output and third-party claims.Confirm chain of title, address licence conflicts and tailor warranties or indemnities to the assets that support the valuation.
Model, cloud and subprocessor dependencies, location, termination, audit evidence, model changes and service continuity.Seek consent, amendment, transition assistance or a post-closing migration plan if a dependency cannot support the buyer’s intended use.
Policies, ownership, AI literacy, logs, testing, monitoring, incident response, complaint handling and escalation records.Set a post-closing governance plan with owners, deadlines and evidence requirements rather than relying on a generic policy.

The European Commission describes the AI Act as a risk-based framework for developers and deployers. It identifies employment, credit scoring and access to essential services among the examples that may be high-risk. See the Commission’s AI Act overview and application timetable.

AI Act review: classify before you value the risk

Do not treat “AI Act compliant” as a sufficient diligence answer. Contractual, sector-specific, data-protection and AI Act obligations must be assessed separately. The investor should identify the system, its intended purpose, the target’s role and the rules that apply now or later. The relevant date can affect both risk allocation and integration planning.

The AI Act’s prohibitions, AI literacy obligations, governance rules, GPAI-model obligations and transparency rules have different application dates from the rules for high-risk systems. The Commission states that Annex III high-risk use cases, including employment and credit-scoring examples, are scheduled to apply from 2 December 2027, while high-risk systems embedded in regulated products have a later date of 2 August 2028. A diligence report should distinguish obligations already applicable from future obligations that could require a funded implementation plan. At the time of publication, the applicable AI Act timetable should be verified against the latest EU legislation and implementation guidance, including the official AI Act Service Desk timeline.

The analysis should also ask whether the target is developing an AI system, placing it on the market, deploying it in its own business, importing it, distributing it or using a third-party service. These labels are not interchangeable with GDPR controller and processor roles. For the contract-facing part of that review, see AI Vendor Contracts in Romania.

GDPR and data review: look beyond the privacy policy

The decisive question is what happens to personal data at each stage of the AI lifecycle. A target may process personal data in training, testing, deployment, monitoring, logs, prompts, support and human review, even where the product is marketed as automated or anonymised.

The review should map the data categories, purposes, retention, recipients, access, transfer mechanisms and contractual roles. Where the use involves profiling, recruitment, credit, insurance, pricing or decisions that may significantly affect individuals, check the actual decision flow and safeguards rather than relying on a generic human-review statement. Article 35 GDPR requires a DPIA where processing is likely to result in a high risk to the rights and freedoms of natural persons; Article 22 has separate rules for certain solely automated decisions.

The European Data Protection Board has also confirmed that the anonymity of an AI model trained with personal data must be assessed case by case. That matters for a target relying on a statement that a model, dataset or output is anonymous. Read EDPB Opinion 28/2024. For the broader framework, see our guide to GDPR compliance when using AI in Romania.

Data, intellectual property and contract rights

AI value is often dependent on rights that sit outside the target’s own code. The investor should trace the legal basis for using data, third-party models, cloud infrastructure, open-source components, output and confidential information.

Review the complete contract suite, not only the signed master agreement. Order forms, online terms, acceptable-use policies, data-processing agreements, security schedules, open-source notices and API terms can all affect the target’s rights. In particular, check whether a provider can use customer or target data for model training, whether the provider can change the model or service unilaterally, and whether the target can export its data and configurations on exit.

Ownership language for AI-generated output should be read carefully. A contractual promise may create a licence or allocation between the parties, but it does not necessarily guarantee exclusivity or copyright protection in every output. The copyright status of AI-generated content may vary depending on the level of human creative input and the applicable jurisdiction. The review should identify the use the target needs to make of the output and whether third-party rights, human authorship requirements, confidentiality or contractual restrictions could limit that use.

What should the investor request in the data room?

  1. Request a current AI inventory. Include internal tools, customer-facing products, models, APIs, plugins, fine-tuning, integrations and material planned features.
  2. Obtain a use-case map. Record intended purpose, users, affected people, decisions, data inputs, outputs, human review and country of deployment.
  3. Collect AI governance records. Ask for role assessments, policies, training records, system documentation, risk logs, testing, monitoring and incident procedures.
  4. Review AI Act screening. Identify prohibited practices, potential high-risk systems, transparency obligations, GPAI dependencies and the applicable timetable.
  5. Map personal-data processing. Review privacy notices, legal bases, Article 22 analysis, DPIAs, processor arrangements, security controls and transfers.
  6. Trace data rights. Check source, licence, consent or other permission for data used in development, testing, fine-tuning and ongoing service delivery.
  7. Review the contract stack. Read supplier, customer, cloud, API, DPA, security, outsourcing and change-control documents together.
  8. Confirm IP and open-source position. Request code provenance, licences, notices, ownership assignments, third-party claims and output-use restrictions.
  9. Test material statements. Compare product marketing, investor materials and customer commitments against the available technical and legal evidence.
  10. Assign the deal response. Separate issues requiring price, warranty, indemnity, condition, remediation, disclosure or post-closing integration action.

How should findings affect the transaction documents?

Translate each material finding into an owner, timing and remedy. A diligence report is useful only if the SPA, investment agreement, disclosure process and integration plan reflect the issues that have been identified.

The appropriate response will depend on the transaction structure and the seller’s ability to remediate. A buyer may need targeted warranties concerning data rights, AI-related regulatory compliance, ownership, contract compliance, absence of claims or material incidents. Confirmed gaps may justify a specific indemnity, a pre-closing remediation covenant, a post-closing plan, a condition or a tailored disclosure. The drafting should not assume that a general compliance warranty captures the actual issue.

Post-closing planning is equally important where the buyer will integrate systems, move data, introduce a new group policy, change suppliers or expand the target’s use case. These changes can alter the GDPR and AI Act analysis. If an assessment is required, the timing should be addressed before the relevant processing or deployment begins. Our DPIA vs FRIA guide explains why those two assessment routes must be screened separately.

When does a separate specialist review become necessary?

A focused AI legal review should be coordinated with corporate, technical, information-security, employment and commercial due diligence when the target develops AI products, relies on proprietary datasets, makes regulated-sector decisions, uses AI in recruitment or credit processes, processes sensitive personal data, markets compliance claims, or has important dependencies on a small number of providers. The workstreams should share the same factual inventory, but each should retain its own legal questions and conclusions.

How Atrium Romanian Lawyers can assist

Atrium Romanian Lawyers can coordinate the legal workstream for AI-related due diligence in a Romanian investment, acquisition or internal reorganisation. The review can cover AI Act role and use-case screening, GDPR and data-contract questions, supplier and customer terms, intellectual property, employment and operational governance, and the translation of findings into transaction documents or an integration plan.

Client experience

AI due diligence during the acquisition of a Romanian technology company

An international investor considered acquiring a Romanian technology company that relied extensively on AI-enabled software products and third-party AI services.

During the due diligence process, the buyer requested confirmation regarding AI Act compliance, data rights, intellectual-property ownership and the target’s dependencies on external AI providers.

The review identified gaps between the target’s public marketing materials and its internal documentation, uncertainties regarding the scope of rights over certain datasets, and contractual limitations affecting the use of third-party AI services after closing.

Atrium Romanian Lawyers coordinated the legal review of the AI use cases, supplier contracts, GDPR implications and intellectual-property position. The findings were translated into targeted warranties, disclosure items and a post-closing remediation plan.

The transaction proceeded with a clearer allocation of regulatory, contractual and operational risks and with a structured roadmap for post-closing compliance measures.

This example has been anonymised and simplified for publication. The appropriate legal analysis depends on the system, data, contract structure and facts of each matter.

Frequently asked questions

Does every investment in a Romanian company need AI due diligence?

No. The scope should be proportionate to the target’s actual use of AI and the importance of that use to the transaction. A company using a limited internal tool may require a focused review. A target selling AI-enabled products, using sensitive data or making decisions affecting people may need a deeper legal and technical workstream.

Is AI due diligence the same as an AI Act compliance audit?

No. AI Act compliance is one part of the review. Transaction diligence also considers ownership, licences, customer commitments, personal data, confidentiality, technical dependencies, product claims, change control and what the buyer will need after closing. The correct scope follows the investment thesis and the target’s operating reality.

Can a seller rely on a supplier’s AI compliance statement?

Supplier information can be relevant evidence, but it does not by itself establish that the target’s own deployment is compliant. The investor should check whether the statement identifies the actual system, model, purpose, data, users, territory, contract terms and responsibilities relevant to the target’s use case.

Should a buyer ask for the target’s DPIAs?

Where the target operates AI systems involving personal data and has conducted or screened for a DPIA, the relevant material should be reviewed subject to confidentiality controls. The question is not simply whether a document exists, but whether it reflects the current processing, risks, safeguards, changes and any residual issues requiring follow-up.

Can AI findings be addressed after closing?

Sometimes. The decision depends on the nature of the issue, legal exposure, urgency, operational dependency and the buyer’s ability to control remediation. A defensible post-closing plan should identify the owner, evidence, budget, deadlines and the effect on continued use. Some issues may need to be resolved before closing or before a planned deployment.

What is the most common gap in AI diligence?

A frequent gap is that the target has a high-level AI policy or vendor contract but no reliable inventory linking systems, use cases, data, roles, evidence and decision owners. The first practical step is usually to build that factual map before drawing legal conclusions or negotiating transaction protection.
Bucharest business district illustrating a share purchase agreement in Romania

Share Purchase Agreement in Romania: Due Diligence, Warranties and Closing Risks

A share purchase agreement in Romania should do more than record the number of shares and the price. It must connect the buyer’s due diligence findings with the conditions for closing, the seller’s warranties, specific indemnities, price mechanics and the corporate and regulatory steps needed to transfer control safely.

In brief: In a Romanian share deal, the buyer acquires the company with its assets, contracts, employees, licences, debts and historical exposure. The SPA therefore allocates risk between buyer and seller. Due diligence identifies the issues; the contract decides whether they must be corrected before closing, reflected in the price, disclosed against warranties, covered by an indemnity or accepted by the buyer. Romanian corporate approvals, ANAF formalities, merger control and investment screening must be tested early because they can change the signing and closing timetable.

This guide is written for foreign investors, international groups, founders and business owners negotiating the acquisition or sale of a Romanian company. It focuses on private acquisitions of shares or social parts, particularly Romanian limited liability companies (SRLs). Listed-company rules, regulated-sector acquisitions, privatisations and public takeovers require additional analysis.

The article complements our procedural guide to changing shareholders in a Romanian company. That guide covers the Trade Register implementation. This one explains how the commercial acquisition should be investigated, negotiated and protected contractually.

What does a share purchase agreement do in Romania?

A share purchase agreement, commonly called an SPA, is the principal contract under which the seller agrees to transfer and the buyer agrees to acquire shares or social parts in a Romanian company. It identifies the securities, price, conditions, closing process and allocation of risk between the parties.

The agreement operates within Romanian contract law and the mandatory rules applicable to the target’s corporate form. For an SRL, the transfer mechanics must be aligned with Articles 202 and 203 of Company Law no. 31/1990 and the applicable registration formalities before the National Trade Register Office (ONRC).

Deal structure
What does the buyer actually acquire?

Select a route to see how the risk profile changes.

Share deal

The buyer acquires the target entity itself. Contracts and assets generally remain with that entity, but so do its historical liabilities and compliance exposure.

Decision pointShare dealAsset deal
What transfersOwnership of the target company.Identified assets, contracts, liabilities or business components.
Historic liabilitiesRemain inside the acquired company and therefore affect the buyer economically.Generally remain with the seller unless assumed by contract or transferred by law.
Contracts and permitsUsually remain with the same legal entity, subject to change-of-control clauses and regulatory rules.May require individual assignment, consent, novation or reissuance.
EmployeesRemain employed by the target.A business transfer may trigger employee-transfer rules and information or consultation duties.
Core documentShare purchase agreement.Business or asset transfer agreement plus asset-specific instruments.

Why must legal due diligence come before the SPA is finalised?

Due diligence should identify the matters that can change the decision to buy, the valuation, the deal timetable or the contractual protection. A report that merely lists documents does not complete the task. Each material finding should be converted into a transaction response.

Share purchase agreement Romania due diligence represented by a green maze with a clear route
Legal due diligence helps the buyer identify risks and determine the appropriate route to a protected transaction. AI-generated illustration.

The scope normally covers corporate title and governance, financing and security, material contracts, real estate, employment, tax, disputes, permits, regulatory compliance, intellectual property, IT, data protection, environmental matters and beneficial ownership. Sector, size and business model determine the emphasis.

Due diligence map
Convert each finding into a deal response

Select a finding to see the appropriate contractual response.

Remediation

Require the seller or target to correct a curable defect before closing and deliver objective evidence that the correction is complete.

WorkstreamKey questionsPossible SPA response
Corporate and titleDoes the seller own the shares? Do the articles of association create pre-emption rights, and are there pledges, options, capital defects or approval restrictions?Title warranty, release condition, shareholder waiver, completion deliverable.
Material contractsDo customers, lenders or suppliers have termination, consent or change-of-control rights?Consent condition, covenant, retention or price adjustment.
EmploymentAre remuneration, dismissals, contractors, collective arrangements and key-person dependencies compliant?Remediation, employment warranty, specific indemnity, retention plan.
TaxAre filings complete? Are there audits, arrears, related-party risks or unsupported tax treatments?Tax covenant, tax warranty, escrow, special indemnity.
IP, technology and dataDoes the target own or validly license critical IP? Are cybersecurity and GDPR controls adequate?Assignment, licence cure, warranty, remediation plan, indemnity.
Disputes and regulationAre there claims, investigations, licences, sanctions, environmental or sector-specific risks?Regulatory condition, conduct covenant, indemnity or exclusion from the deal.

Which clauses matter most in a Romanian share purchase agreement?

The SPA should describe the transaction as one coherent mechanism. Definitions, price, conditions, warranties, disclosure, indemnities, limitations, covenants and closing deliverables must work together. Imported English-law wording should not be used without checking how it operates under the chosen governing law and Romanian mandatory rules.

Clause navigator
How does each protection work?

Select a clause family to see its transaction function.

Warranties

Contractual statements about the target, shares and business. Their value depends on scope, disclosure, knowledge qualifiers, repetition, claim rules and available recovery.

ProtectionPrincipal functionDrafting question
WarrantyAllocates risk if a contractual statement about the target or business is inaccurate.What is warranted, when is it true, and how do disclosure and seller knowledge qualify it?
Specific indemnityAllocates a defined known or identified exposure.What event triggers payment, which losses are covered and do general limitations apply?
Condition precedentPrevents closing until a necessary event, consent or approval occurs.Who controls satisfaction, what evidence is required, and when may either party terminate?
Pre-closing covenantControls how the target operates between signing and closing.Which actions need buyer consent without giving the buyer unlawful premature control?
Limitation regimeSets time limits, thresholds, caps, exclusions and claim procedure.Which claims are carved out, and does the recovery structure match the seller’s credit risk?

How should the purchase price be structured?

The price clause should explain both the headline value and the route from that value to the amount paid. A fixed price is not necessarily simple if debt, cash, working capital, leakage, earn-outs, holdbacks or currency conversion remain unresolved.

MechanismHow it worksMain negotiation risk
Locked-boxPrice is based on historic accounts at an agreed date, protected by a no-leakage covenant.Reliability of the accounts, leakage definition and permitted payments.
Completion accountsPrice adjusts after closing by reference to closing debt, cash, working capital or other metrics.Accounting policies, hierarchy of rules, timetable and expert determination.
Earn-outPart of the consideration depends on future performance or milestones.Control of the business, metric manipulation, extraordinary items and information rights.
Escrow or holdbackPart of the price is retained or deposited to support identified obligations or claims.Release triggers, duration, permitted deductions and insolvency protection.

A buyer should not treat escrow as a substitute for a coherent claims regime. The SPA should state whether recovery is limited to the escrow, whether the buyer may set off, how competing claims are handled and what happens when the escrow expires.

What is the difference between signing and closing?

Signing creates the contractual commitment. Closing completes the agreed transfer and payment once the applicable conditions are satisfied or waived. They may occur on the same day in a simple transaction, but regulatory approvals, third-party consents, financing or restructuring often require a split process.

Transaction roadmap
From exclusivity to effective control

Select a stage to review the principal legal control.

Term sheet

Align structure, valuation, exclusivity, confidentiality, process and principal conditions before the parties spend heavily on diligence and drafting.

Which Romanian approvals and filings can affect closing?

The regulatory analysis should begin before the SPA timetable is agreed. A condition drafted after signing cannot restore leverage or time already lost.

Corporate approval and ONRC registration

For an SRL transfer to an outside buyer, Article 202 of Company Law no. 31/1990 applies together with the target’s articles of association. The parties should verify statutory approval thresholds and any pre-emption or consent rights created by the articles of association, as well as pledges and other restrictions. The applicable ONRC registration formalities and the update of the company’s shareholder register should be built into the completion process.

ANAF notification and tax-debt safeguards

The practical scope of Article V of Law no. 239/2025, as amended by Government Emergency Ordinance no. 13/2026, should be verified in light of the transaction structure and current ONRC and ANAF practice. Although the regime was introduced in the context of transfers affecting company control, registration practice during 2026 has raised questions regarding its application to a broader range of SRL share transfers, as discussed in this analysis of emerging ONRC practice. The parties should confirm the current notification, tax-certificate, guarantee and registration requirements before signing and again before filing.

Merger control

An acquisition of sole or joint control may constitute an economic concentration. Under Competition Law no. 21/1996, the Romanian thresholds are generally met where the combined worldwide turnover of the undertakings concerned exceeds EUR 10 million and at least two undertakings concerned each achieved Romanian turnover exceeding EUR 4 million in the previous financial year. The EU Merger Regulation may apply instead where its thresholds are met. Closing before the required clearance can expose the parties to gun-jumping risk.

Investment screening

Romania’s investment-screening regime under Government Emergency Ordinance no. 46/2022 was substantially amended by Government Emergency Ordinance no. 17/2026. The general value threshold is now EUR 5 million, but a transaction below the threshold may still be examined if it may affect security, public order or EU projects or programmes. The rules can apply to EU and non-EU investors, and the filing contribution is EUR 5,000 where an authorisation application is required. Sector, investor, control, value and transaction structure must be screened early.

Sector approvals, lender consents, foreign-subsidy review or contractual change-of-control notices may also be relevant. The SPA should allocate responsibility, information, cooperation, remedies and the long-stop date for each approval.

What should happen at closing?

Closing should be a coordinated exchange, not a loose collection of signatures. The SPA should identify every deliverable, who provides it, its agreed form and whether all actions are deemed simultaneous.

  1. Confirm conditions. Record satisfaction or valid waiver of every closing condition.
  2. Approve the transfer. Deliver the required shareholder and corporate resolutions.
  3. Transfer the shares. Execute the required instruments and update the shareholder register.
  4. Pay the consideration. Follow the funds flow, escrow and debt repayment arrangements.
  5. Release security. Deliver releases of share pledges, guarantees or target security where agreed.
  6. Change governance. Coordinate resignations, appointments, powers of attorney and bank mandates.
  7. Deliver control items. Transfer corporate books, credentials, keys, seals and agreed records.
  8. Complete filings. Submit ONRC and ANAF documents, together with beneficial-owner filings where required under the applicable transparency rules, within the relevant timetable.

What limitations should apply to seller liability?

Seller limitations often include a de minimis threshold, basket, aggregate cap, time limits, mitigation, exclusion of double recovery and a formal claim procedure. Tax, title, authority, fraud and specific indemnities may have different limits. The commercial result depends on how these provisions interact, not on any one headline cap.

The buyer should also test recoverability. A contractual claim against a seller with no accessible assets may provide little protection. Escrow, holdback, bank security, parent guarantee or warranty and indemnity insurance may be considered depending on transaction size and risk.

A buyer’s pre-signing checklist

  1. Define the acquisition perimeter. Confirm percentage, target entities, securities and excluded items.
  2. Verify title and authority. Check ownership, encumbrances, approvals and signatory powers.
  3. Complete risk-focused due diligence. Prioritise issues that affect value, continuity or closing.
  4. Translate findings into protections. Allocate each material issue to remediation, price, condition, warranty, indemnity or withdrawal.
  5. Select the price mechanism. Define accounting rules, leakage, debt, cash, working capital and dispute resolution.
  6. Screen regulatory approvals. Review merger control, investment screening, sector approvals and third-party consents.
  7. Align signing and closing. Specify conditions, conduct rules, long-stop date, termination and closing deliverables.
  8. Test recovery. Check caps, time limits, exclusions, seller credit and available security.
  9. Plan filings and integration. Prepare ONRC and ANAF filings, beneficial-owner filings where required under the applicable transparency rules, governance steps and day-one actions.

The bottom line

A Romanian SPA should be the final expression of the buyer’s investigation and the parties’ negotiated risk allocation. The strongest agreement is not the longest. It is the one that identifies what is being bought, states how price is calculated, prevents closing before essential approvals, allocates known and unknown risks clearly and gives the parties an executable closing process.

Planning the acquisition or sale of a Romanian company?

A focused transaction review can cover deal structure, legal due diligence, SPA negotiation, regulatory screening, signing, closing and Romanian corporate implementation.

Book a Consultation

Frequently asked questions

Is a share purchase agreement mandatory in Romania?

A written transfer instrument is normally required to document and implement the transaction. In a negotiated acquisition, the SPA is the central agreement because it also records price mechanics, conditions, warranties, indemnities and closing. The required form and supporting corporate documents depend on the target’s legal form and transaction structure.

What is the difference between an SPA and a shareholders’ agreement?

The SPA governs the acquisition of shares and the allocation of transaction risk between buyer and seller. A shareholders’ agreement governs the continuing relationship among shareholders after the investment, including governance, reserved matters, funding, transfers, deadlock and exit. A minority investment may require both documents.

Can signing and closing occur on the same day?

Yes, where no unsatisfied conditions or approvals require a split process. If merger control, investment screening, financing, third-party consent or pre-closing remediation is required, signing normally precedes closing and the SPA must regulate the interim period and long-stop date.

Does due diligence remove the need for warranties?

No. Due diligence and warranties serve different functions. Diligence helps the buyer identify and evaluate risk. Warranties allocate contractual risk for inaccurate statements, subject to disclosure and limitations. Known issues may require remediation, a price adjustment or a specific indemnity rather than reliance on a general warranty.

When is Romanian investment-screening approval required?

The analysis depends on the investor, target activity, transaction structure, control or durable participation, sensitive sector and investment value. The general threshold is EUR 5 million after OUG no. 17/2026, but lower-value transactions may still be examined where security, public-order or relevant EU interests may be affected.

What happens after the SPA closes?

The parties must complete the agreed corporate, Trade Register and ANAF steps, as well as beneficial-owner filings where required under the applicable transparency rules. They must also release or retain escrow as applicable, implement governance changes and perform post-closing covenants. Price-adjustment, earn-out, indemnity and integration obligations may continue long after legal ownership changes.

Disclaimer: This article provides general information and does not constitute legal or tax advice. The correct structure, approvals, tax treatment and contractual protections depend on the parties, target, sector and facts of each transaction.

AI Notice: AI-assisted content, reviewed and approved by a qualified Romanian lawyer.